All Categories
Featured
Table of Contents
To asses risk Waydev allows you to determine how most likely it is a specific commit will trigger problems. In this case, there specify data points that you need to take into account, such as the commit's size, how far do the changes spread, as well as the changes' depth. Constant Combination (CI) and Continous Advancement (CD) are important in today's engineering environment due to the fact that they make sure that your group provides software application in an iterative type.
How to Reduce Multi-Cloud Waste Using Predictive Models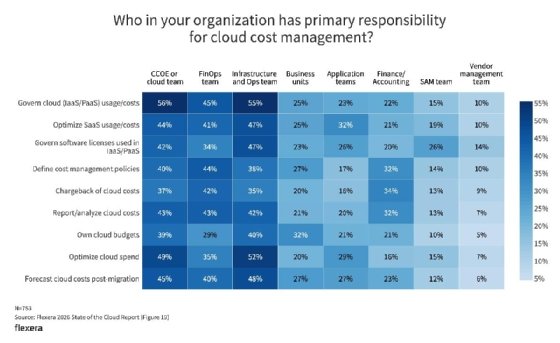
Our service instantly gathers data from the Constant Combination and Continous Development pipelines and tracks Gitlab repos, allowing you to examine details without needing any type of manual input. This is an exceptional method to monitor DevOps efficiency by focusing on DORA metrics. By automating these procedures and measurements, you may have a clear view of how deployment is going, examine what effects burn-down rates, what causes bottlenecks, and how to resolve them.
With Waydev's Task Costs report, you have constant insights on how work is advancing and how things look economically. This enables you to reallocate resources to ship on time or optimize expenses and interact project status to business leaders. When done right, the aligns company requirements with innovation processes, enabling Engineering Supervisors to optimize efficiency and analyze threats.
IT governance concentrates on setting strategic instructions, policies, and oversight. IT management includes everyday operations, carrying out jobs, and administering systems and services. Key stakeholders are executive leaders, IT supervisors, end users from service units, and process owners. A governance council or committee offers oversight. Training should cover structure principles, brand-new policies and treatments, governance functions and obligations, and any governance tools or systems being executed.
Optimizing Enterprise Expenditures in 2026
Risk management identifies hazards, evaluates effects, and develops mitigation techniques. It makes sure governance adequately addresses info security, catastrophe healing, and regulative compliance.
Efficient IT governance is a key component of overall service strategy and corporate governance as a governance, threat and compliance (GRC) policy. IT governance manages governance and risks while preserving compliance with market and federal government policies. Enhancing IT governance needs the ideal mix of IT financial investments, policy and workers. It assists organizations match their IT objectives with company objectives.
As organizations increase their IT investments, the value of a strong IT governance policy boosts. Chief information officers (CIOs) drive IT governance strategy alongside other crucial stakeholders in the C-suite.
In this postWhat is IT governance and why does it matter?Why worksIT governance essential for service success?What are the 5 actions to execute effective IT governance?What are the IT governance best practices that drive results?How does IT governance work for small businesses?Why reputable IT governance is a company advantage Reliable IT governance lines up innovation decisions with business strategy, controls threat, and guarantees IT resources are utilized efficiently. This guide covers each step in useful information, together with the frameworks, tools, and best practices IT leaders utilize today.
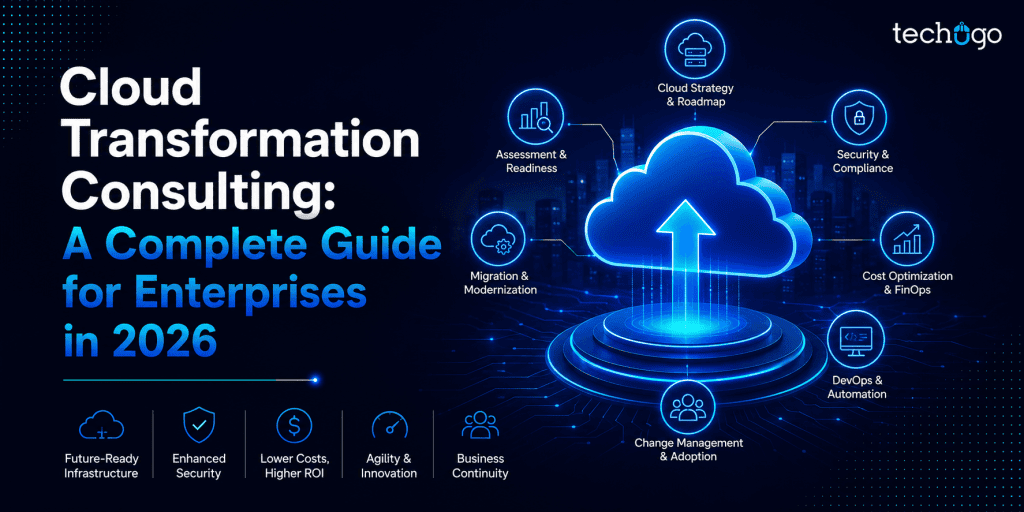
Advantages of Centralized Cost Governance
Appoint clear accountability for each governance domain. Structure Primary focus Finest fit for IT governance and management, risk control, audit preparedness Large enterprises, managed markets IT service management aligned to organization requirements Organizations with a mature IT service function International standards for IT service management and business IT governance Organizations looking for certified, globally recognized governance CMMI(Capability Maturity Design Combination)Process enhancement rated on a scale of 1 to 5 Organizations benchmarking and improving advancement or delivery capability COSO (Committee of Sponsoring Organizations of the Treadway Commission)Internal control and business threat management Organizations focusing on monetary controls and scams deterrence CIS( Center for Internet Security)Controls Cybersecurity and infrastructure strength Organizations strengthening technical security posture Lots of companies combine structures. Governance that is not determined does not enhance.

Latest Posts
Leveraging Performance Metrics to Boost Cloud ROI
Analyzing IT Performance Through Advanced Governance Frameworks
Maximizing IT Performance Through Strategic Planning